Independent cyber security consultancy
Clear, practical cyber security advice.
Vortigen Cyber helps organisations understand their exposure, respond to incidents and improve their security.
Our core service offering focuses on independent security testing, cloud security reviews, incident response, forensic investigation and board-level advice and guidance.
Assurance that stands up to scrutiny
- 01Security testing
- 02Incident response
- 03Cloud security reviews
- 04Board and executive advice
Direct access
Work directly with the person responsible for your engagement.
There is no sales queue or unnecessary account-management layer. From the first conversation through delivery and follow-up, you work directly with an experienced practitioner who understands your requirements and remains accountable for the work.
Contact VortigenServices
Focused support for real security decisions.
Security assessments
Independent testing of internal and external infrastructure, networks, wireless and business-critical systems.
Learn moreWeb applications and APIs
Manual testing of authentication, access control, business logic, APIs and sensitive data handling.
Learn moreMicrosoft cloud reviews
Practical reviews of Entra ID, Microsoft 365, Azure, Dynamics 365 and Power Platform.
Learn moreIncident response and forensics
Support to understand what happened, scope the impact, preserve evidence and make recovery decisions.
Learn moreSecurity advice and governance
Independent advice for boards and leaders who need a clear view of risk, priorities and preparedness.
Learn moreNot sure where to start?
A short conversation can establish the issue, the likely options and whether Vortigen is the right fit.
Start a conversationExperience
Experienced advice without the layers.
Vortigen Cyber is led by the founder and former CEO of 7 Elements. Vortigen’s experience includes work with critical national infrastructure, FTSE 100 businesses and public-sector organisations.
About VortigenApproach
Thorough where it matters. Clear throughout.
- 01
Understand
Start with the organisation, its systems and the decisions the work needs to support.
- 02
Test
Use controlled, proportionate testing agreed in advance.
- 03
Validate
Review findings manually and reduce false positives.
- 04
Prioritise
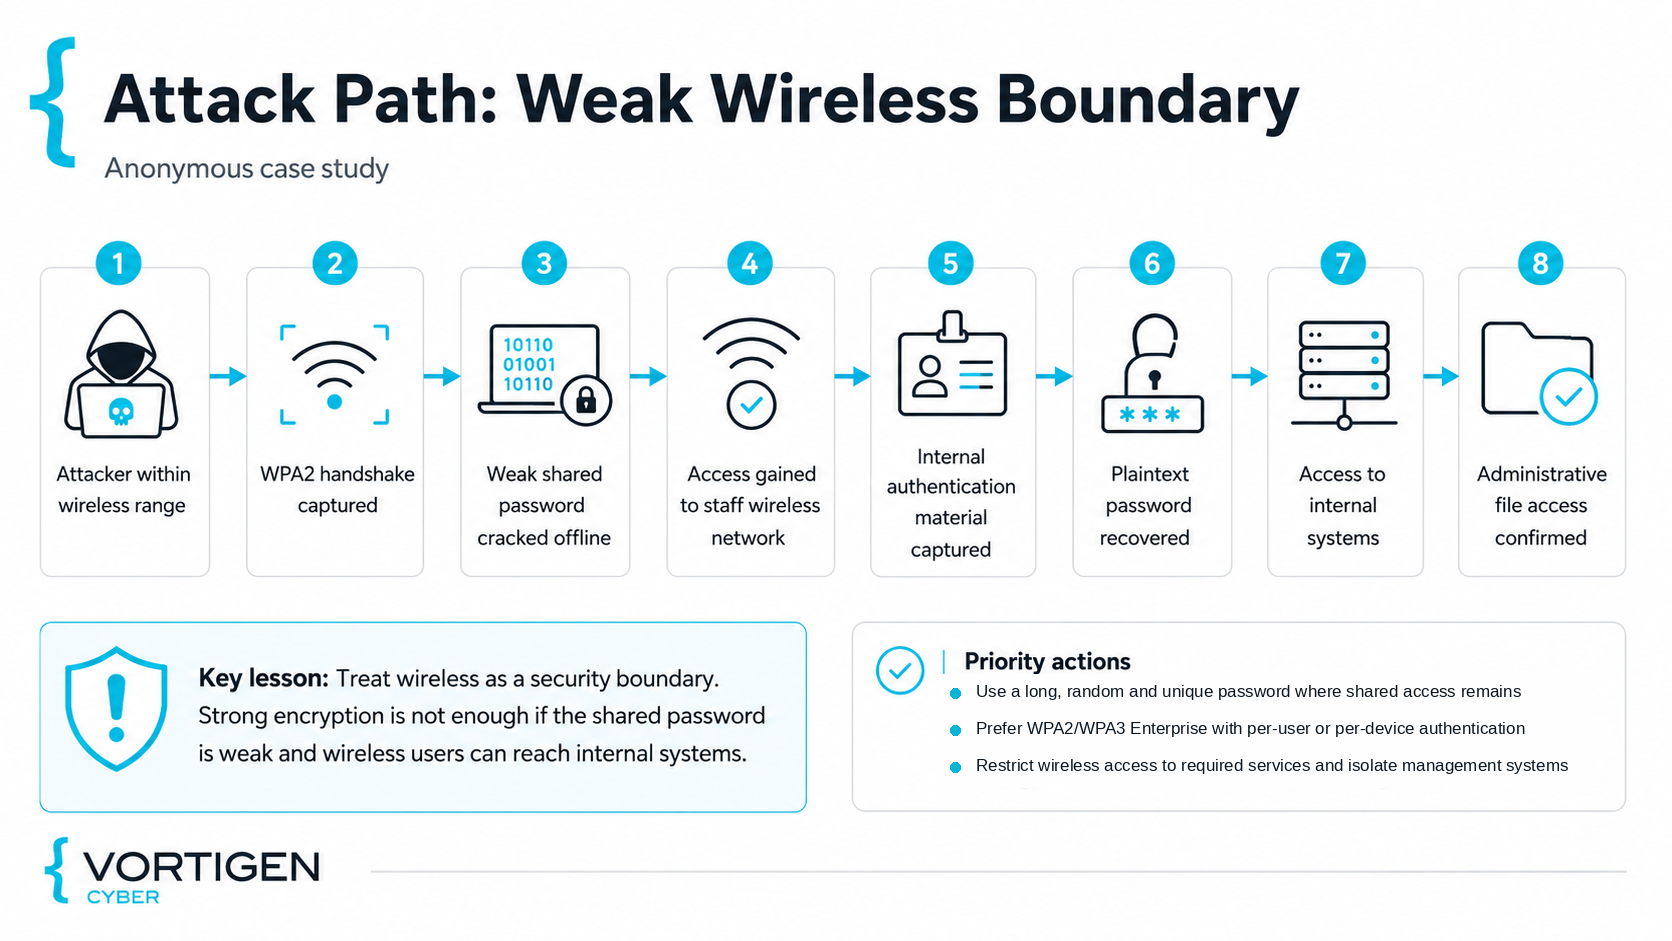
Focus first on the attack paths and controls that materially change risk.
- 05
Explain
Write clearly for technical teams, decision-makers and boards.
Start a conversation
Speak directly with an experienced practitioner.
No sales team and no unnecessary handover. Explain what is happening and get a straightforward view of the next step.